Following the recent security vulnerabilities affecting technologies such as PHP, Node.js, nginx and the Linux kernel, many TU Delft systems remain inaccessible from outside the campus network. More clarity is now available regarding the process for restoring external access.
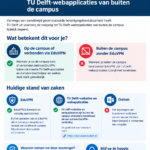
What does this mean?
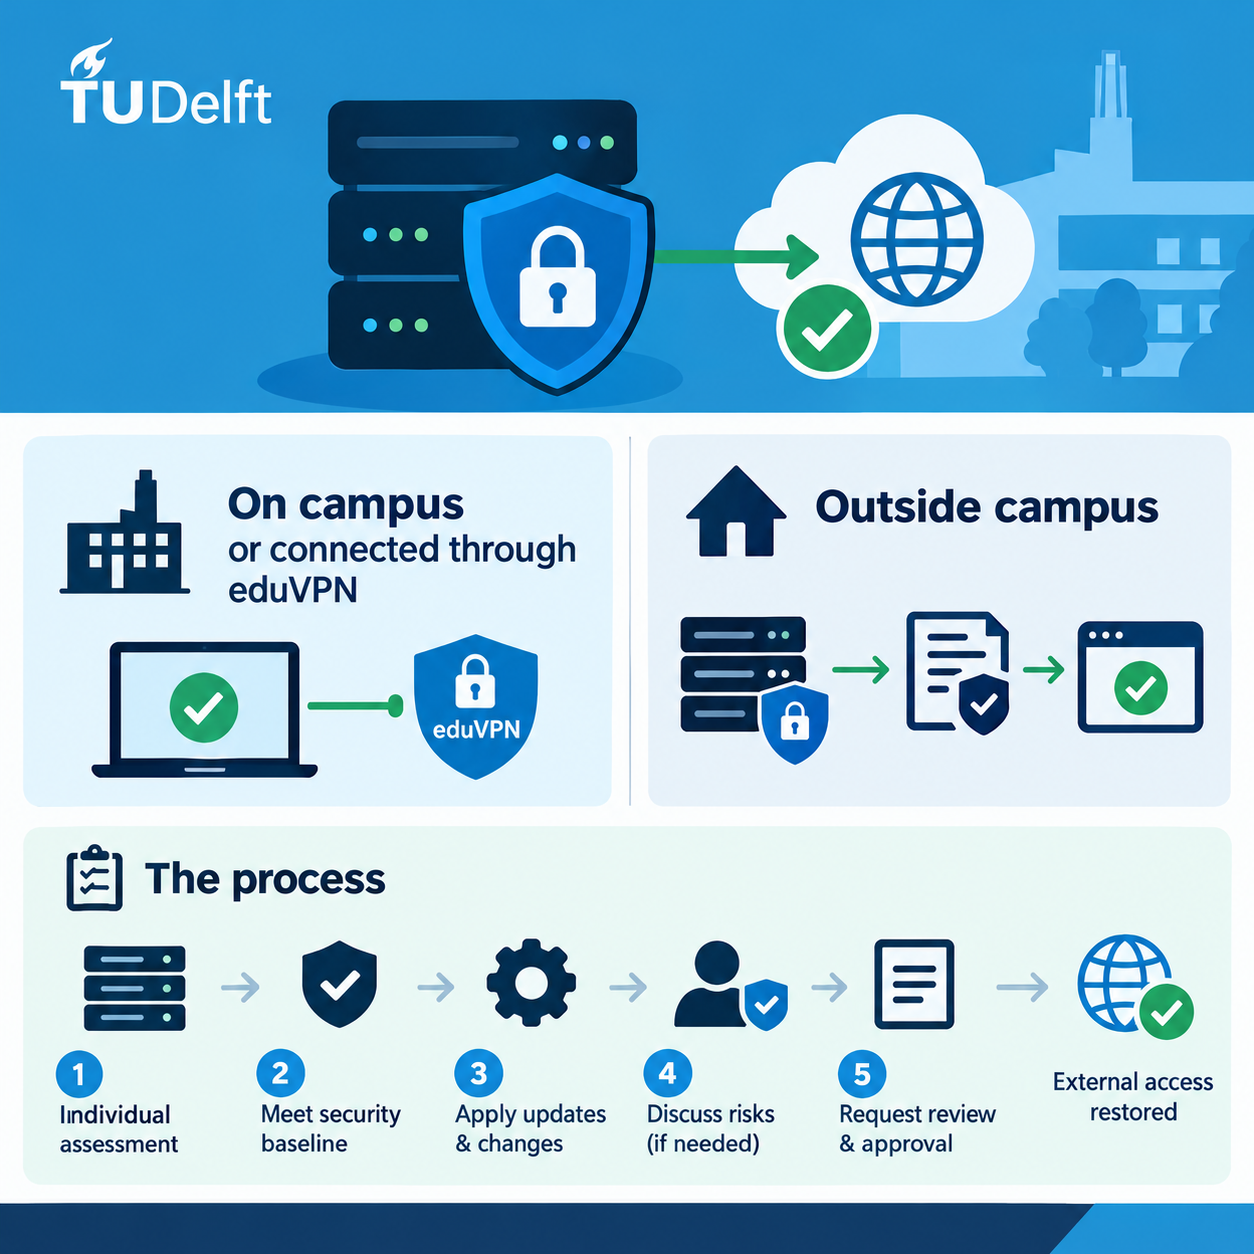
On campus or connected through eduVPN
If you are working on campus or connected through eduVPN, affected systems remain accessible as usual.
Outside campus
External access can only be restored once the system complies with the established security baseline and the request for external access has been approved.
What do you need to do?
Before external access can be restored, each server must be individually assessed against the required security standards.
Please keep the following in mind:
- Submit a separate request for each server.
- Verify in advance that the server complies with the approved security baseline.
- Apply required security updates and configuration changes where necessary.
- Discuss any identified risks and mitigating measures with your Information Security Officer (ISO) if a risk assessment is required.
- Submission of a request does not automatically restore external access. Each request will be reviewed and validated before approval.
Support
If you have questions regarding the security requirements, risks or required measures, please contact your faculty’s Information Security Officer (ISO) or the Security team. Contact details are available on the Contact-Security page.
For technical assistance, please contact the ICT Service Desk.
More Information
Detailed information about the current situation, security requirements, available guides and the application process can be found on the intranet page: https://intranet.tudelft.nl/-/https-/intranet.tudelft.nl/php-informatiepagina

 English
 Dutch